Source: Fortune.com
Summary
A $387 million security breach at crypto exchange Bitget has been linked to North Korean hackers, who exploited a backend system to authorize fraudulent withdrawals. CEO Gracy Chen said the attackers did not steal private keys but manipulated internal approvals. Bitget paused withdrawals and is working with Mandiant and SlowMist to investigate. The loss estimate increased after additional transactions were identified on Zcash and TRON networks. BGB, Bitget’s native token, fell 7% but later recovered slightly. North Korean-linked hackers stole $2 billion in crypto in 2025, according to Chainalysis.
Our Reading
The numbers tell one story.
Bitget lost $387 million in a hack blamed on North Korea.
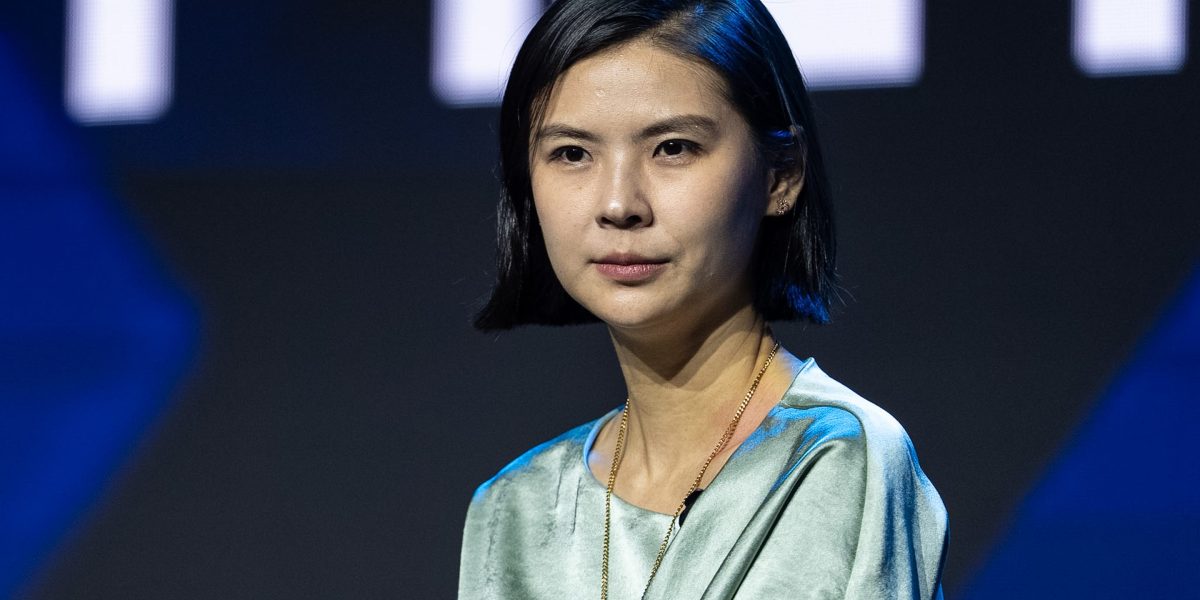
CEO Gracy Chen said the breach involved backend systems, not private keys.
Bitget paused withdrawals and partnered with security firms.
North Korean hackers are now the top crypto threat, stealing $2 billion in 2025.
Author: Evan Null
Bitget’s $387 Million Breach
On Thursday night, Bitget, a major cryptocurrency exchange, suffered a security breach that drained over $387 million from the platform. The attack is now the largest cryptocurrency hack of the year. The incident has raised concerns about the security of digital assets and the growing threat of cyberattacks in the crypto sector.
The breach was discovered during a three-hour livestream on X, where CEO Gracy Chen explained that North Korean hackers exploited a backend system used to process wallet transactions. The attackers managed to make fraudulent withdrawals appear legitimate without stealing private keys, which are essential for moving crypto. This method of attack highlights the vulnerabilities in internal approval systems.
Bitget has since fixed the vulnerability and paused withdrawals while it reviews the platform’s security. The loss estimate was revised after additional transactions were identified on networks such as Zcash and TRON, which are used for privacy-focused and stablecoin transfers. This indicates that the breach may have been more extensive than initially thought.
Following the breach, Bitget announced a partnership with third-party experts Mandiant and SlowMist to investigate the incident. The exchange also launched a recovery-bounty program offering rewards of up to 5% for funds successfully frozen or recovered. A real-time tracking dashboard was also released to help researchers and other platforms identify the attacker’s wallets.
Despite the loss, Bitget said its user protection fund, which holds over $464 million, is sufficient to cover the current loss if the stolen funds cannot be recovered. This suggests the company is attempting to reassure users and maintain confidence in its platform. However, the incident has once again highlighted the risks associated with storing digital assets on centralized exchanges.